Cybersecurity researchers have recently highlighted an increasingly deceptive phishing technique known as a “Homoglyph Attack” (IDN Homograph Attack). Attackers register fake domains using foreign script characters that look virtually identical to standard Latin letters—for example, replacing the Latin letter “
c” with the Cyrillic letter “с” to spoof miсrosoft.com or аmazon.com. On small mobile screens or during quick clicks, the difference is almost impossible to spot with the naked eye.To help you catch these look-alike traps before clicking an unfamiliar link, our URL Inspection (/en/check) tool now features automated Homoglyph Attack detection paired with an unmistakable “poop stamp” high-risk warning!
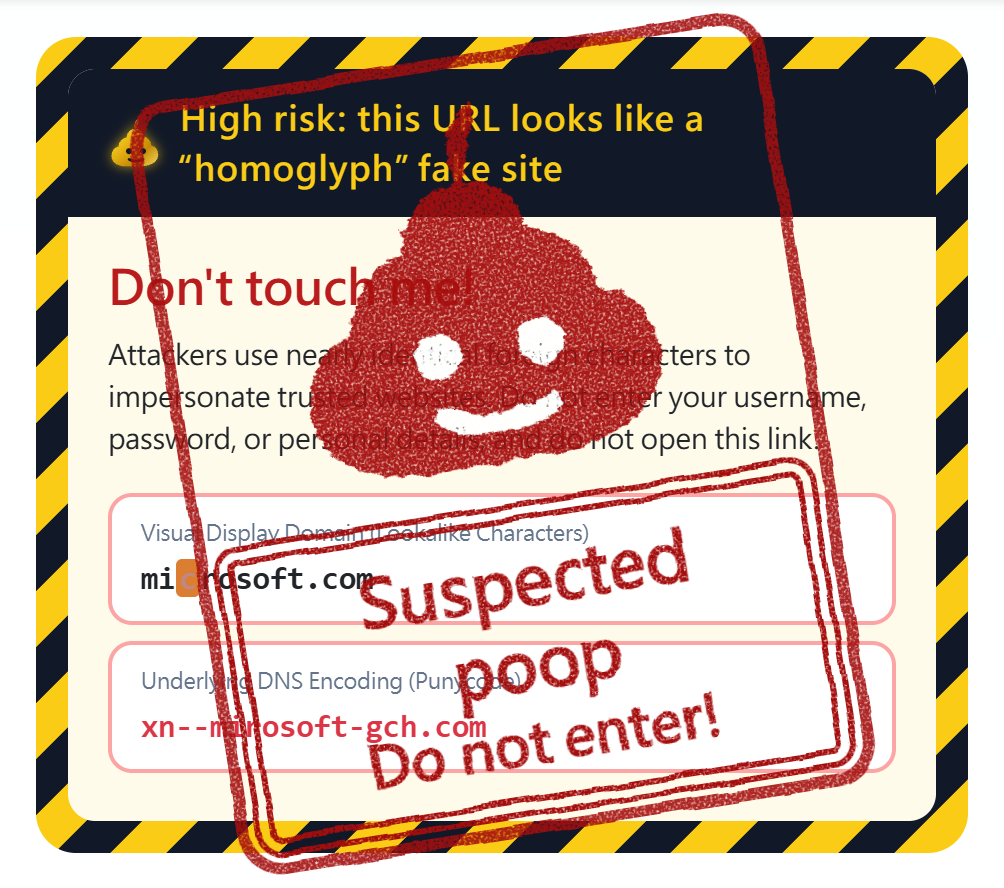
- Automated Cross-Script Confusable Detection: Inspects both the target URL and every hop in its redirect chain for confusable scripts—including Cyrillic, Greek, Armenian, Cherokee, and Coptic—as well as mixed Latin and non-ASCII domain labels.
- High-Impact Caution Tape & “Poop Stamp” Alert: When a high-risk homoglyph domain is detected, the top summary pod is replaced by an animated yellow-and-black caution-tape card shouting “Don’t touch me!” and stamped right across the center with a red “Suspected poop · Do not enter!” seal.
- Blinking Red Character Highlight & Punycode Comparison: Places the “Visual Display Domain” side by side with the “Underlying DNS Encoding (
xn--Punycode)” and highlights the exact imposter characters in blinking red. - Automatic OpenGraph Preview Suppression: Automatically hides the target webpage’s OpenGraph preview card on homoglyph hits so phishing sites cannot use stolen brand logos or titles to lower your guard.
2. Practical Tips to Stay Safe from Homoglyph Phishing
- Never click unfamiliar login, parcel delivery, or payment links directly from SMS messages, emails, or social chats.
- Copy and paste suspicious links into URL Inspection (/en/check) first. If you see the caution tape and poop stamp warning, close the link immediately and never enter your credentials.
Try the upgraded protection anytime at URL Inspection!